Your Application Has Ten Years of Knowledge. Is It Ready for AI Agents?
SIMPLEX INSIGHTS · APPLICATION MODERNISATION & AGENTIC ENGINEERING
A CTO is reviewing next year’s technology budget. A business-critical application, built over twelve years, still serves its customers well. Its workflows embody years of commercial decisions and hard-won business knowledge. The technology is not necessarily obsolete.
Yet changes take longer than expected. Two experienced developers can explain almost every unusual behaviour, but little of that reasoning is documented. New colleagues hesitate to change unfamiliar modules. A modest enhancement requires extensive investigation because no one is certain what else might break.
The team has experimented with AI coding assistants. The initial results look promising, but generated changes miss business rules, require substantial correction or expose gaps in the tests. Management asks whether agents could reduce dependence on expensive engineering resources.
Before choosing between maintenance, a rewrite and greater automation, the CTO needs a clearer understanding of the application itself.
The application is valuable. The dependency is the concern.
Age does not determine software quality. A ten- or fifteen-year-old application may be stable, well maintained and commercially important. Replacing it risks losing behaviour that customers rely on but nobody has fully specified.
What happens if the two most knowledgeable engineers leave? Can a new developer distinguish an intentional exception from an accidental workaround? Does anyone know how a change to one interface will affect another service?
Source code shows what a system does, not always why. Tests, tickets, architecture records and people each hold part of the explanation. That makes continuity a business concern, not simply an engineering inconvenience.
Alongside technical debt sits knowledge debt
Technical debt makes change harder through coupling, fragile tests, old dependencies or unclear boundaries. Knowledge debt is a related problem: the gap between what an organisation needs to understand about its application and what it can confidently retrieve, explain and verify.
Business rules may be scattered across code, Jira, Confluence, old design documents and experienced developers’ memories. Sources conflict or refer to previous releases. More documentation alone will not solve this. Teams need current, trusted knowledge linked to its owners and the work it supports.
Without that foundation, new developers and AI agents repeatedly rediscover the same decisions. The cost appears in onboarding, review effort, rework and slower delivery.
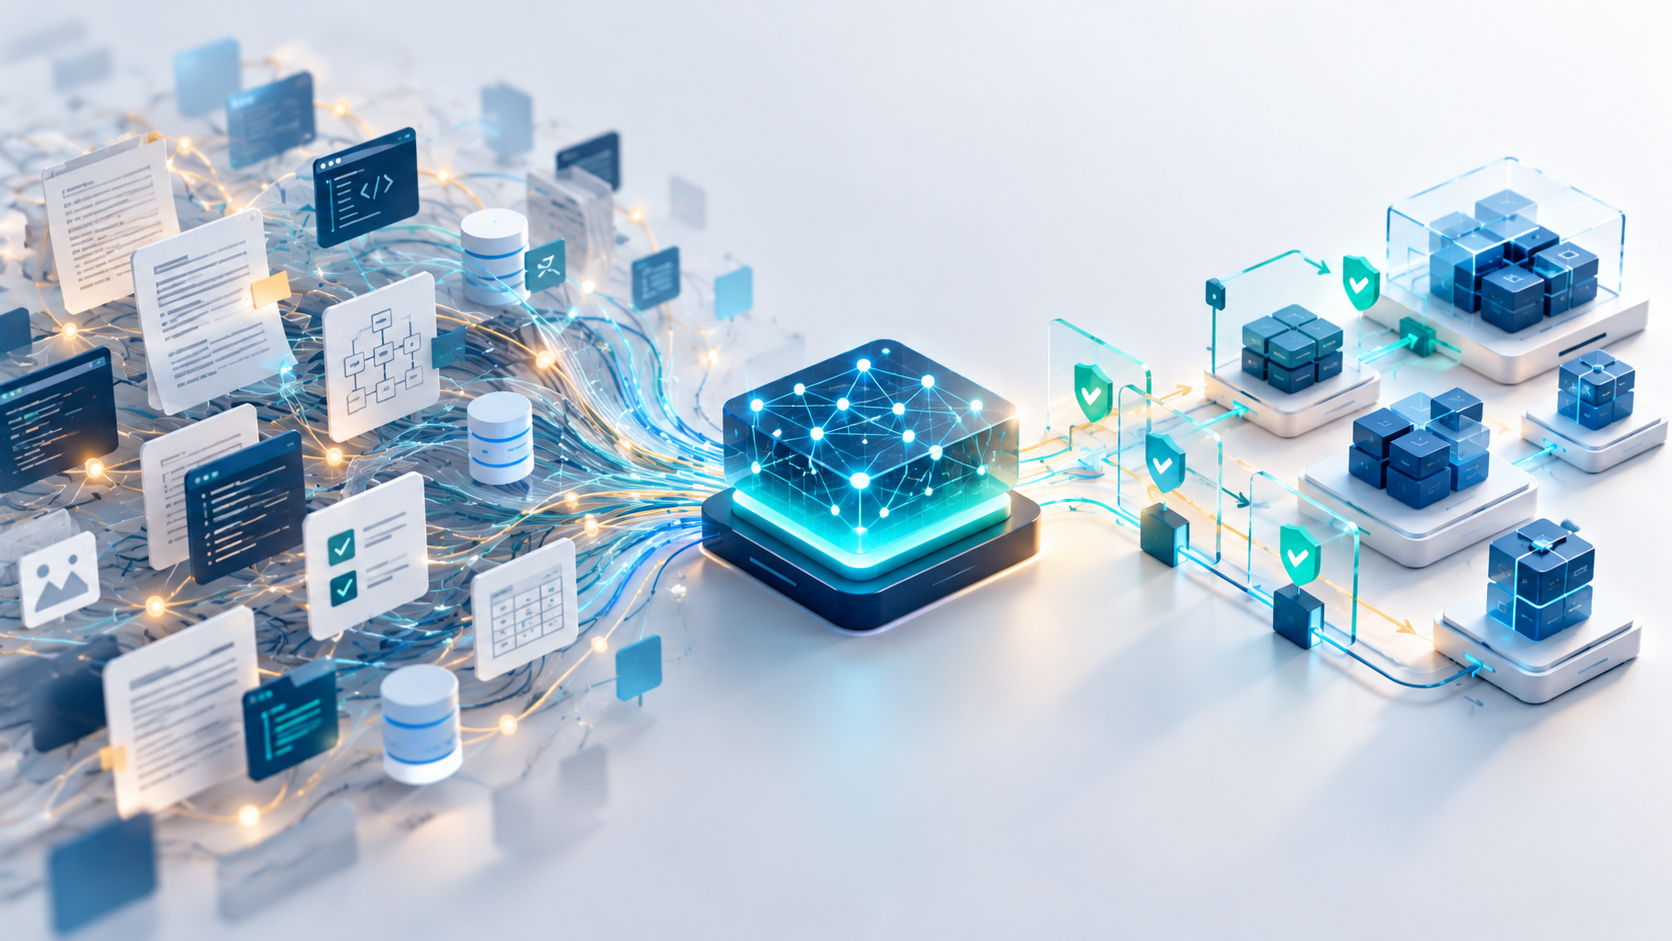
Why adding coding agents is not enough
A coding assistant can draft plausible changes from the context it receives. A reliable agentic engineering capability must also understand architectural constraints, business intent, interfaces, engineering standards and what constitutes an acceptable outcome.
An agent can misunderstand a requirement and generate tests that reinforce the mistake. Producing code faster does not necessarily mean delivering accepted changes faster. Reproducible builds, trustworthy tests, independent verification, appropriate access and human approval remain essential.
Google’s 2025 DORA research describes AI as an amplifier of existing organisational strengths and weaknesses. McKinsey’s 2026 work on agentic delivery likewise emphasises consistent architecture, connected knowledge and well-structured engineering processes. NIST’s Secure Software Development Framework provides established security practices, but it cannot resolve undocumented business requirements.
Better models can help. They do not automatically replace the business knowledge carried by experienced engineers.
Three horizons: understand, enable, operate and evolve
Horizon 1 — Understand: establish the baseline
Start with an evidence-based view of application health and readiness. Examine architecture, dependencies, maintainability, testing, build reliability, security, operating risks and the concentration of essential knowledge. Understand the time, cost and uncertainty involved in making typical changes.
This is not an exercise in finding reasons to rewrite. It identifies what should be preserved, where improvement would help and which activities are already suitable for AI assistance.
The outcome should inform a credible investment decision: retain, refactor, modularise, modernise selectively or eventually replace, with the risks and trade-offs made visible.
Horizon 2 — Enable: build the foundations
Use the findings to reduce unnecessary dependency. Capture critical business rules and architectural decisions. Reconcile approved sources across repositories, tickets and documentation, making ownership and currency clear.
Improve engineering guidance, reusable practices, development environments and meaningful automated tests. Establish security boundaries, responsibilities and independent checks before increasing agent autonomy. Identify bounded work where the application is understood well enough to test the approach.
The objective is not documentation for its own sake. It is to help people make and review changes confidently—and give AI tools a trustworthy context in which to assist.
Horizon 3 — Operate and Evolve: supervised engineering
Once those foundations are sufficiently reliable, introduce limited engineering work through a supervised Engineering Pod. Complementary roles provide structure: an Architect holds context and design constraints; a Developer implements approved changes; an independent QA Reviewer validates behaviour and tests against acceptance criteria; and a Security Reviewer considers relevant risks and safeguards.
These are responsibilities within an engineering process, not a promise that agents replace developers. Humans retain accountability for decisions and acceptance. Begin with manageable maintenance tasks, assess the results and extend responsibility when evidence supports it.
Our earlier Insight, When agents write the code, who verifies the outcome?, explores the distinct importance of verification once agents begin producing changes.
Preserve value rather than default to replacement
Sometimes replacement is right: the technology cannot meet future needs, support has ended, or continued maintenance carries unacceptable cost or risk. Sometimes targeted refactoring or gradual separation of components offers better value.
AWS’s guidance on incremental modernisation illustrates one approach to changing established applications without a single disruptive rewrite. It is an option, not a universal prescription.
An assessment should determine the best direction. AI-assisted engineering can support that direction; it should not decide it.
Where Meridian fits
Meridian, developed by Simplex, connects application understanding, AI governance and continuing engineering improvement. Existing Meridian Readiness Assessments provide an evidence-based starting point for examining technology, engineering organisation, controls and AI readiness.
Meridian Factory is our developing Software Factory direction, exploring application assessment, technology-appropriate engineering practices, controlled execution, specialised Engineering Pods, independent verification and traceable engineering evidence. It is not presented as a finished commercial factory product.
An organisation may use assessment findings to strengthen its own engineering setup or consider a Meridian-enabled capability. Different models and deployment approaches—including externally hosted and private or self-hosted options—may suit different requirements, subject to validation of security, technical capability, integration and cost.
Measure the outcomes that matter
Success is not the amount of code generated or tokens consumed. It is the time and total cost of an accepted change, the effort spent reviewing and correcting work, escaped defects, maintenance predictability and how easily another engineer can continue where a colleague left off.
That is the practical meaning of more continuous, connected and controlled engineering: preserving accumulated knowledge, reducing concentration of risk and making application evolution more dependable.
If your most experienced developers left tomorrow, how confidently could your organisation continue developing its critical applications—with or without AI?
Discuss your application’s engineering readiness
If this challenge feels familiar, an Application Health & Agentic Engineering Readiness Assessment can help establish an evidence-based starting point, without presuming a rewrite or a particular AI solution.
Further reading and sources
- Google DORA — State of AI-assisted Software Development (2025). AI as an amplifier of organisational capabilities.
- McKinsey & Company — Rewiring software delivery for the agentic era (28 May 2026). Engineering roles, application context and connected knowledge.
- AWS — Strangler fig pattern, Prescriptive Guidance. An incremental application-modernisation approach.
- NIST SP 800-218 — Secure Software Development Framework (2022). Established secure-development practices.
Simplex Insight · Published November 2026. The opening example is illustrative and does not describe a specific client or engagement. This article provides general engineering and governance guidance.